
Pakistan’s 5G Reaches 24 Cities With 1,782 Sites
October 25, 2026
Pakistan’s AI policy is approved, published, and referenced in nearly every government tech briefing. The Cabinet signed off on it on July 31, 2025. The six pillars are listed. The ambitions; one million AI professionals by 2030, a National AI Fund, Centres of Excellence; are on the record.
What is also on the record, if you read past the press releases: there is no binding AI law. There is no enacted data protection statute. There is no enforcement body with actual authority. There is no legal definition of what counts as a high-risk AI system, who is liable when one causes harm, or what consent is required before training a model on Pakistani users’ data.
For founders building AI products in Pakistan right now, this is not an abstract policy debate. It is the actual operating environment. And it cuts both ways: no law means no compliance burden today, but it also means no rules of the road, no investor certainty, and a real risk that a law arrives suddenly; mid-product and redraws everything.
This blog explains exactly where Pakistan’s Pakistan AI policy stands, what is missing, what is coming, and what founders should be doing about it in the meantime.
What the National AI Policy 2025 actually delivers
The National AI Policy 2025 is a genuine step forward. It is the government’s clearest statement yet on where it wants AI development in Pakistan to go, and it is organized around six pillars: AI Innovation Ecosystem, Awareness and Readiness, Secure AI Ecosystem, Transformation and Evolution, AI Infrastructure, and International Partnerships and Collaborations.
The concrete commitments include a National AI Fund to finance startups and research, AI Centres of Excellence (CoE-AI) to be established at universities and research institutions, regulatory sandboxes for testing AI products in a controlled environment, and the goal of training one million AI professionals by 2030. A National AI Council is proposed as the apex body to oversee implementation, and a Policy Implementation Cell is meant to coordinate execution across federal and provincial governments.
The policy also endorses compute and data infrastructure development, including plans for a national data repository and high-performance computing resources to support AI model training.
The policy aims to train one million AI professionals by 2030, fuel AI startups through Innovation and Venture Funds, and foster thousands of civic and local AI projects. That vision is genuinely ambitious for a country at Pakistan’s stage of digital development.
The timeline question, however, is already a problem. The short- and medium-term goals outlined in the AI Policy action matrix appear overly ambitious and, in some cases, impractical; eight months of 2025 had already passed with little indication of progress when the policy was published, suggesting a lack of alignment between the policy’s ambition and ground realities including institutional readiness, resource availability, and implementation capacity.
That is not a cynical reading. It is the Digital Rights Foundation’s own assessment, drawn from a close review of the document.
What a policy cannot do and why that matters
Here is the key distinction that gets lost in most coverage of this topic: a policy is a statement of intent. A law is a set of enforceable rights, duties, and penalties.
Pakistan’s National AI Policy tells you what the government wants to happen. It cannot compel a company to do anything, cannot penalize a developer who ignores it, cannot give a citizen a legal claim when an AI system harms them, and cannot create the oversight body with actual authority to enforce any of its principles.
While Pakistan’s National AI Policy 2025 prioritizes innovation and growth, it lacks enforceable safeguards to protect rights, allowing monitoring, censorship, algorithmic bias, and technology-facilitated harms to flourish unchecked, according to a study by the Digital Rights Foundation. Drawing on 11 focus group discussions with 79 participants and 60 survey responses, the study found that 65 percent of participants feared loss of privacy, 63 percent expressed concern about disinformation, and half worried about AI-enabled monitoring.
Real-world harms are already visible. Research participants shared examples including women targeted by AI-generated deepfakes, AI-fuelled disinformation exacerbating sectarian violence, and journalists relying on tools like ChatGPT and DALL-E while fearing job displacement and automation bias.
None of these harms has a legal remedy specifically designed for AI in Pakistan. That is the gap.
The policy does not categorize AI by risk level. This omission means there are no clear prohibitions on the most harmful AI practices, such as social scoring or exploitative manipulation; harms the EU AI Act bans outright. The policy remains a non-binding strategy and lacks legal prohibitions against AI that infringes fundamental rights or explicit requirements to prevent discrimination and bias.
Think of it this way: the EU has the AI Act, which bans certain applications, mandates conformity assessments for high-risk systems, and creates a whole enforcement architecture. Pakistan has a document that says it agrees with the general principle of responsible AI. Those are very different things.
The missing law: where the Personal Data Protection Bill stands
The most consequential missing piece of Pakistan’s AI governance puzzle is the Personal Data Protection Bill. The National AI Policy leans on this bill heavily, it references data protection principles, privacy safeguards, and the need for consent frameworks, all of which would need this bill to have any legal force.
As of September 2026, Pakistan has no enacted comprehensive Personal Data Protection Act. Drafts, including the Personal Data Protection Bill 2023 and earlier versions, have not been passed into force as a full privacy statute.
The bill’s journey has been anything but smooth. The personal data protection bill, which was passed by the Federal Cabinet of Pakistan, was returned by the Parliament to the Ministry of Information Technology and Telecommunication on the basis that it had been introduced by a single member of government. It went back to the drawing board. It has since been revised and the updated draft has again cleared the Federal Cabinet, but as of the time of writing, it has not passed both houses of Parliament.
Pakistan currently has not enacted specific data protection legislation similar to that enacted in other countries. An amendment to PECA was passed in 2025, and a draft of the Personal Data Protection Bill 2023 has been introduced by the Ministry of Information Technology and Telecommunications, but it remains a draft pending Parliamentary passage and Presidential assent.
The draft bill would define “personal data” broadly, create a National Commission for Personal Data Protection (NCPDP), and require data controllers to give data subjects detailed notices about data collection, purpose, retention, and their rights. However, the bill remains mired in Parliament. For now, no independent data protection authority exists. Under PECA, enforcement of data offences falls to the Federal Investigation Agency and the Pakistan Telecommunication Authority.
For AI startups, this creates a specific operational problem: the policy they are expected to align with references a legal framework that does not yet exist. How do you demonstrate consent compliance when there is no consent law? How do you build data governance processes around a bill that may pass next month, next year, or in a different form entirely?
The honest answer is: you prepare for the law that is coming, not the one that currently exists.
The newest piece on the table: The National Data Governance Policy
In June 2026, a new document entered the picture. Pakistan published a draft National Data Governance Policy on June 26, released by the Ministry of Information Technology and Telecommunication for public consultation, seeking to create common standards across the federal government, establish new institutions to oversee data governance, and lay the foundations for a digital public infrastructure in which government agencies exchange information through a common framework rather than isolated databases.
There is important fine print here that founders need to understand. This policy is about government data, not private-sector products. Its primary audience is federal agencies, not startups.
The policy makes clear that government agencies would no longer treat data as their own property. “Public bodies are custodians, not proprietors,” it says. “Custodianship carries the duty of stewardship: to protect, to maintain quality, to make discoverable, to share lawfully, and to disclose proportionately.”
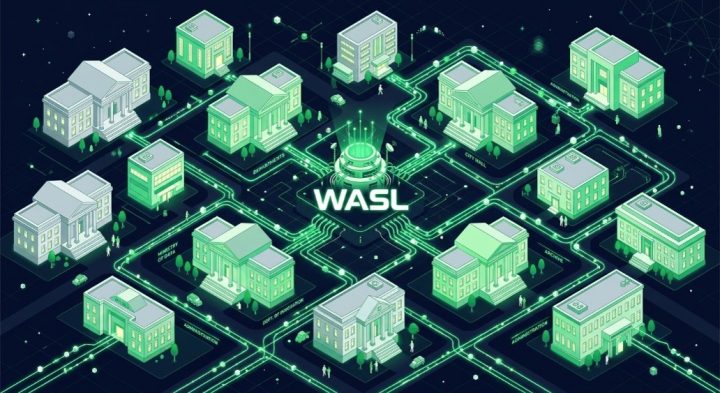
That is meaningful for AI applications that rely on government datasets; health, land records, identity, transport, and similar public-sector data. The policy proposes a National Data Exchange called WASL through which federal agencies would share information securely, and introduces a “once-only” principle: citizens should not need to submit the same information to the government more than once.
The framework sets out a risk-based approach for the government’s use of artificial intelligence, requiring greater oversight of systems that could have legal or similarly significant effects on citizens.
On cross-border data transfers, the policy proposes that sensitive government and personal data generally remain hosted and processed within Pakistan, while allowing offshore processing only in specified circumstances subject to approval and safeguards.
That data localization principle, if it eventually applies more broadly to private-sector AI, would have significant implications for startups using cloud infrastructure outside Pakistan. Watch this space.
Implementation would be overseen by the Pakistan Digital Authority, which would designate a National Chief Data Officer, require federal agencies to appoint their own Chief Data Officers, and establish a National Data Governance Council to coordinate implementation across the federal government and provinces.
The policy still requires Federal Cabinet approval before it takes effect. It is a consultation draft. But its emergence signals the direction of travel and gives founders a preview of the compliance vocabulary that is coming.
Sector rules that already bite
Before anyone concludes that Pakistan’s startup environment is a full-blown regulatory vacuum, one correction is necessary: sector-specific regulators have been active, and their requirements already touch AI products in meaningful ways.
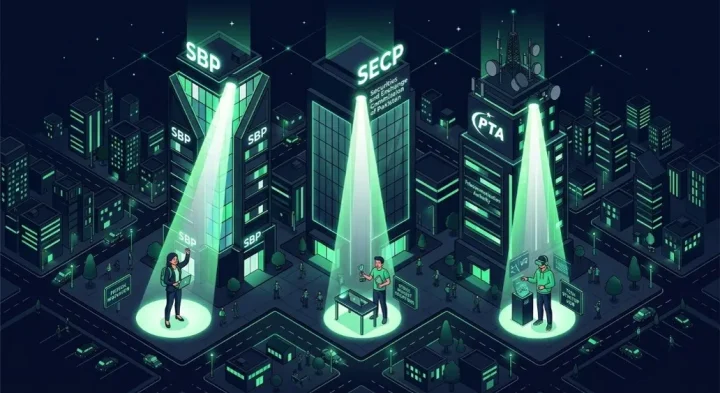
Figure 5 – SBP, SECP, and PTA are not waiting for an AI law; their rules already apply to your product.
For fintech and banking:
The State Bank of Pakistan’s evolving supervisory signals and the Securities and Exchange Commission of Pakistan’s proposed algorithmic-trading framework have collectively created a new regulatory environment that every fintech founder, bank risk committee, and investor must navigate before putting an AI model into production. The National AI Policy explicitly directs the SBP and SECP to develop domain-specific rules consistent with its principles, which means sector-specific AI guidance from these regulators is coming.
In 2026, the SBP and SECP jointly issued Circular No. BPRD/CSD/2026/09, mandating comprehensive cybersecurity audits for all licensed commercial banks, digital wallets, and regulated fintech companies, requiring data residency audits and incident response certifications by Q4 2026. If your AI product sits inside the financial services stack, this is a live compliance requirement right now.
For telecoms:
PTA governs telecom and ISP data under the Pakistan Telecommunication (Re-organisation) Act. If your AI product uses telecom data, customer traffic patterns, or works with a licensed operator, PTA’s licensing conditions apply.
For all sectors:
PECA 2016 and its 2025 amendments create criminal liability for unauthorized disclosure of personal data. This is not a comprehensive privacy law; it is a cybercrime statute, but it is the most enforceable data protection instrument currently in existence in Pakistan. Ignoring it is not an option.
The pattern across SBP, SECP, and PTA is consistent: these regulators require transparency about how data is processed, impose outsourcing and data-handling rules on licensed entities, and expect firms to demonstrate consumer protection compliance. AI tools embedded in regulated products are already within scope.
What no document covers yet
Here is the honest catalogue of what remains completely unaddressed in Pakistan’s regulatory landscape as of mid-2026.
Liability for AI harms:
If an AI system makes a wrong credit decision, misidentifies someone in a facial recognition system, or produces a deepfake of a real person, who is legally responsible? The National AI Policy does not answer this. No law does. Despite referencing AI adoption in decision-making across ministries and the public and private sectors, the policy omits any legal mechanisms for accountability or liability. There is no clarity on who bears responsibility when AI systems cause harm, make biased decisions, or violate rights.
Algorithmic bias:
The policy mentions fairness as a value. It does not create any obligation to test for bias, any standard for what acceptable bias looks like, or any remedy for people harmed by biased AI decisions. This is particularly significant in sectors like credit scoring, hiring, and healthcare.
Consent for training data:
Building a model on Pakistani users’ data without their knowledge is not currently prohibited by any AI-specific rule. The PECA provisions on data disclosure offer some protection, but there is no clear legal framework governing the collection and use of data for AI training purposes.
Synthetic media and deepfakes:
Eighty-four percent of Pakistani newsrooms use AI tools, with documented cases of women being targeted by AI-generated deepfakes and AI-fuelled disinformation exacerbating sectarian violence. There is no specific legal instrument addressing synthetic media creation or distribution.
Who enforces any of this:
The proposed AI Directorate within the National AI Policy has no defined legal status, no clear regulatory powers, and no enforcement authority. The AI Council is positioned as the apex body overseeing implementation, but there is no indication of a legal or statutory basis establishing the Council’s authority, powers, or governance. Without formal legal backing, the Council’s decisions and directives may lack enforceability.
Why this gap is expensive for startups; not just an inconvenience
Founders sometimes read “no AI law yet” as a green light. It is more complicated than that.
Investor and enterprise due diligence is getting stricter:
International VCs and enterprise clients now routinely ask about data governance, AI ethics frameworks, and compliance readiness as part of due diligence. A startup that cannot articulate its data handling practices; even in the absence of a Pakistani law requiring it; is leaving deals on the table. The compliance question is not “are you breaking a Pakistani law?” It is increasingly “are you building something that a regulator, anywhere, will have a problem with?”
The law will arrive mid-product:
Pakistan’s data protection bill has been circulating for years. It will pass eventually. When it does, startups that have not already mapped their data flows, documented their consent practices, and designed their products with privacy in mind will face the most expensive outcome: retrofitting compliance into a live product at scale. That is significantly harder and costlier than building it in from the start.
Unclear compliance targets create competitive disadvantage:
When the rules are vague, larger incumbents can absorb legal uncertainty more easily than startups. A bank with a legal team can navigate ambiguity. A six-person startup cannot. Clear law, even demanding law, tends to level the playing field.
Cross-border exposure is real:
Many Pakistani AI startups are building products for international markets, serving users in the EU, UK, US, or UAE. Those users are already protected by GDPR, UK GDPR, and other frameworks. The absence of a Pakistani AI law does not protect a Pakistani startup from GDPR obligations if it processes EU residents’ data. The compliance burden exists regardless of domestic law.
A founder’s gap-year checklist: what to do before the law arrives
You cannot wait for the bill to pass. Here is what responsible founders should be doing right now.
Map your data:
Know exactly what personal data your product collects, where it is stored, how long it is retained, who has access, and whether it crosses borders. This is the foundation of any compliance programme and the first thing any regulator or investor will ask for.
Document consent:
Even without a legal requirement, record how and when users give consent to data collection and use. The draft Personal Data Protection Bill requires informed, specific consent. Building that into your product now means you will not need to rebuild it when the law passes.
Document your models:
Keep records of what data was used to train your AI models, what the model does, how it was tested, and what its known limitations are. This is the basis of the transparency and explainability requirements that are almost certainly coming. It also helps you identify and address bias before it becomes a liability.
Audit your vendor contracts:
If you use third-party AI infrastructure: cloud providers, API-based AI services, data annotation services; review your contracts for data handling clauses. Does your vendor agree to process data only as instructed? Are there data residency obligations? Who owns the data you send through their systems? These questions matter more as localization rules get closer.
Plan for localization:
The draft National Data Governance Policy proposes that sensitive government and personal data generally remain within Pakistan. If that principle extends to private-sector data, which is not guaranteed but is a real possibility, startups using AWS, GCP, or Azure for data storage outside Pakistan will need a contingency. Know where you stand and what switching would involve.
Get your sector right:
If your AI product touches financial services, check your SBP and SECP obligations. If it uses telecom data, understand your PTA exposure. Sector regulators are ahead of the general AI regulatory framework, and their requirements are already live.
What to watch next
Three developments will define the regulatory picture for Pakistani AI startups over the next 12 to 18 months.
The Personal Data Protection Bill in Parliament:
This is the single most consequential legal development to track. When it passes and the current draft clears the Federal Cabinet, it will create the first comprehensive consent, data handling, and enforcement framework in Pakistan. The version that passes may differ from current drafts, but the core principles (consent, data minimization, individual rights, a regulatory body) are likely to survive.
The institutional home for AI oversight:
The National AI Policy proposes an AI Directorate, an AI Council, and a Policy Implementation Cell. None of these has statutory authority yet. Watch for whether any of them gets a formal legal footing through an ordinance, an amendment to an existing act, or a dedicated AI governance bill. The institutional question determines whether the policy’s principles can be enforced.
The National Data Governance Policy’s fate:
The June 2026 draft goes to the Federal Cabinet next. If approved in something close to its current form, it establishes data localization principles, a National Data Exchange, Chief Data Officers across government, and a risk-based framework for government AI use. The precedents it sets for government data handling will influence how private-sector obligations are eventually framed.
Sector-specific guidance from SBP and SECP:
Both regulators are expected to issue AI-specific guidance for their sectors, consistent with the National AI Policy’s direction. Fintech founders in particular should watch SBP supervisory signals closely; the central bank has been the most active of Pakistan’s regulators in signaling AI expectations.
Conclusion
Pakistan has made real progress on AI governance in a short time. The National AI Policy 2025 establishes a national framework, names the right priorities, and creates the architecture for an AI ecosystem. The draft National Data Governance Policy adds a serious layer of data infrastructure thinking. Sector regulators are moving.
But a policy is not a law. And the gap between what the policy promises and what any court, regulator, or citizen can enforce today remains very wide. No liability framework. No enacted data protection statute. No statutory AI oversight body. No rules on consent for training data, algorithmic bias, or synthetic media.
For startups, the message is not “relax while there are no rules.” It is “build as if the rules are coming; because they are.” The founders who treat the gap-year as a preparation window rather than a free pass will be the ones whose products survive contact with the law when it finally arrives.
The policy is written. The law is next. The question is whether you will be ready when it lands.